News and Events
Network Access Control Solutions Philippines: Managing Devices Connecting to Enterprise Networks
What Are Network Access Control Solutions?
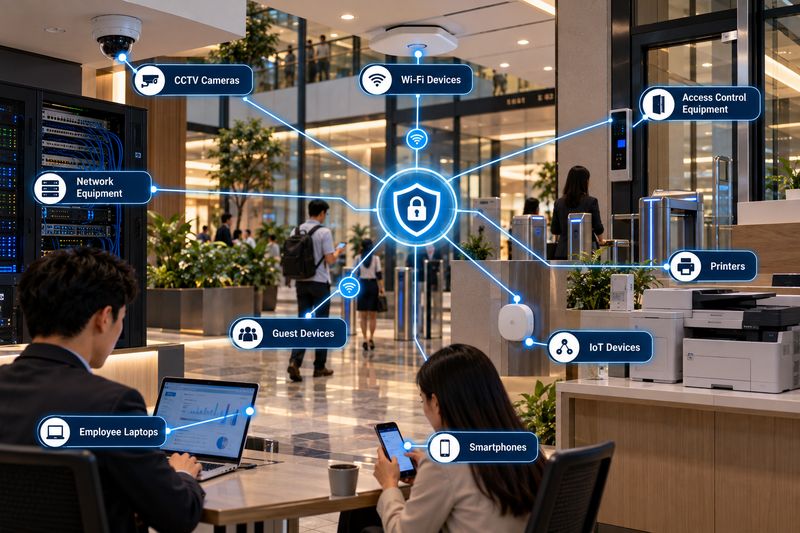
Network Access Control Solutions Philippines are cybersecurity technologies used to manage which users and devices are permitted to connect to an organization’s wired and wireless networks. Commonly known as NAC, these solutions help organizations apply access policies to laptops, mobile devices, guest devices, network equipment, and other endpoints before or while they connect to business resources.
Unlike physical access control systems that manage entry through doors, Network Access Control focuses on digital network access. It can help identify connected devices, authenticate users, evaluate device status, and determine which parts of the network each connection should be allowed to reach.
A NAC environment may work with network switches, wireless infrastructure, authentication services, directories, firewalls, and other security platforms.
Foxcon Total Solutions, Inc. provides enterprise network, firewall, Wi-Fi, monitoring, and security infrastructure solutions that can support structured network access environments.
Why Choose Network Access Control Solutions?
Modern organizations connect many different types of devices to the same network infrastructure. Employee laptops, smartphones, guest devices, printers, cameras, access control equipment, IoT devices, and other endpoints may all require different levels of access.
Network Access Control Solutions Philippines provide a more structured way to manage these connections. Instead of treating every connected device the same, NAC policies can assign access based on factors such as user identity, device type, connection method, location, security status, or organizational role.
Guest users can also be separated from internal business resources, while unknown or non-compliant devices may be restricted, redirected, or placed in a limited network segment, depending on the selected platform and policy design.
NAC can complement Network Security Solutions, Enterprise Firewall Solutions, Enterprise Wi-Fi Solutions, Network Monitoring Solutions, Network Switch Solutions, and Enterprise Network Architecture.
How Network Access Control Solutions Work
A Network Access Control environment evaluates a connection when a user or device attempts to join the network. Depending on the architecture, this can occur through wired switch ports, enterprise Wi-Fi, remote access, or other supported network entry points.
Authentication may use usernames and passwords, device certificates, directory information, endpoint identity, or other supported methods. The NAC platform then compares the connection against configured policies before determining the level of network access that should be assigned.
An authorized employee device might be placed on a corporate network with access to approved applications, while a guest device could be assigned to an isolated internet-only segment. An unknown, unmanaged, or non-compliant device may receive limited access until the issue is resolved.
The exact architecture varies by platform, but switches, wireless controllers, authentication servers, directories, firewalls, and policy engines may work together to enforce access decisions across the network.
Network Access Control Solutions Safety & Trust
NAC policies can directly affect business connectivity, so they should be introduced carefully. A policy that is too restrictive or incorrectly configured can prevent legitimate employees, applications, or operational devices from accessing the resources they need.
Before broad enforcement, administrators should define user groups, device categories, access roles, exceptions, authentication methods, and failure behavior. Testing is especially important in environments containing printers, cameras, building systems, medical equipment, or other devices that may not support the same authentication methods as employee computers.
Administrative access to the NAC platform should also be restricted. Policy changes, authentication settings, device classifications, and integrations can affect large sections of the network, making configuration control and documentation important.
Foxcon Total Solutions, Inc. supports network projects through Engineering and Design, Supply and Installation, Project Implementation, System Integration, Testing and Commissioning, Network Monitoring, Preventive Maintenance, and related technical services.
Network Access Control Solutions Tips
-
Inventory users and devices first. Know what already connects before applying new policies.
-
Separate different device groups. Employees, guests, IoT, cameras, and building systems may need different access.
-
Define policies before enforcement. Avoid building rules directly in production without testing.
-
Coordinate NAC with switches and Wi-Fi. Enforcement depends on compatible network infrastructure.
-
Plan for devices that cannot authenticate normally. Some operational equipment may require alternate identification methods.
-
Restrict administrative access. NAC policy changes should be limited to authorized technical personnel.
-
Document exceptions. Temporary bypasses should not become permanent unknown configurations.
-
Review policies regularly. User roles, devices, and business applications change over time.
-
Test failover behavior. Understand what happens when authentication or NAC services become unavailable.
Profile the Device Before Giving It Network Access
A device successfully connecting to the network does not mean it should automatically receive the same access as a trusted employee computer. An unknown laptop, unmanaged mobile device, camera, printer, or IoT endpoint may require a completely different network policy.
NAC platforms can use available identity and device information to help classify endpoints before assigning access. Depending on the technology, this may involve credentials, certificates, device attributes, authentication records, or observed network characteristics.
The classification should then connect to a practical access policy. For example, a corporate laptop may require access to internal applications, while a surveillance camera may only need communication with specific recording servers and management systems.
Building access around the role of the device helps reduce unnecessary connectivity and makes network segmentation easier to manage as the number of connected endpoints grows.
Frequently Asked Questions
What is Network Access Control?
Network Access Control is a security approach used to determine which users and devices are permitted to connect to specific parts of an organization’s network.
Is Network Access Control the same as physical access control?
No. Physical access control manages entry through doors or secured areas, while NAC manages access to wired and wireless digital networks.
Can NAC manage guest devices?
Yes. Compatible NAC systems can place guests on separate or limited network segments according to predefined organizational policies.
Can Network Access Control work with Wi-Fi?
Yes. NAC can work with compatible enterprise wireless infrastructure to authenticate users and apply network access policies.
Can NAC control wired connections?
Yes. Compatible NAC platforms can work with managed switches and authentication mechanisms to control access through wired network ports.
What happens to an unknown device?
Depending on the policy, an unknown device may be denied access, placed in a restricted segment, redirected for registration, or given limited connectivity.
Does NAC replace a firewall?
No. NAC controls who or what can connect and what level of network access is assigned, while firewalls primarily enforce traffic rules between network zones, systems, or external connections. The two can work together.
Why should NAC policies be reviewed regularly?
Users, devices, applications, network infrastructure, and security requirements change over time. Regular reviews help keep access rules aligned with actual operational needs.
Test the Policy With Real Devices Before Full Enforcement
A NAC rule can appear correct on paper but behave differently once it encounters the variety of devices already connected to a production network. Employee laptops, printers, cameras, IP phones, wireless devices, and building systems may all authenticate and communicate differently.
Before full enforcement, technical teams should test representative devices from each important category. The test should confirm authentication, device classification, assigned network role, access to required services, and behavior when the device does not meet the expected policy.
Special attention should be given to operational equipment that cannot easily be upgraded or reconfigured. Blocking a critical device because it does not support a preferred authentication method can create an operational problem rather than improve security.
A staged rollout with monitoring allows policies to be refined before they affect the entire organization.
Control Network Access Around Identity, Device Type, and Business Need
A properly planned Network Access Control Solutions Philippines environment should coordinate user identity, device classification, authentication, network segmentation, switches, wireless infrastructure, firewalls, policy enforcement, exceptions, and monitoring as one complete access strategy.
Foxcon Total Solutions, Inc. can support enterprise network planning, NAC integration, switching, Wi-Fi infrastructure, firewall deployment, testing, monitoring, documentation, and preventive maintenance for commercial and institutional environments.
📞 Contact us today to discuss your network access control and enterprise security requirements.
📍 Serving businesses in Cebu, Metro Manila, and nationwide.
🌐 Explore Foxcon’s solutions to learn more about our services.
References
1. Cisco – What Is Network Access Control (NAC)?
https://www.cisco.com/site/us/en/learn/topics/security/what-is-network-access-control-nac.html
2. Fortinet – What Is Network Access Control?
https://www.fortinet.com/resources/cyberglossary/what-is-network-access-control
3. Sangfor – Network Access Control (NAC)
https://www.sangfor.com/glossary/cloud-and-infrastructure/network-access-control-nac
4. Purple – Network Access Control Solutions
https://www.purple.ai/en-gb/blogs/network-access-control-solutions
5. Illumio – Network Access Control (NAC)
https://www.illumio.com/cybersecurity-101/network-access-control-nac